Batch 1 Sold Out · Internal Test Release · Phase: Security Hardening
Next milestone: Batch 1 ships · end of January 2027
2026-10-09 Build

Project update: Guardian, Vault OS, testing, and the risks we are managing

TL;DR The project is progressing steadily, and internal prototype units have been delivered to our team. Two more units for internal testing will follow at the end of October. Next week we are presenting the Vault to potential partners at two conferences in the U.S., and one Vault customer will have an in-person testing session to give us real-world feedback. We will ask him to share his uncensored feedback with all customers on an upcoming webcast. However, AI usage limits will cause a further delay to Batch 1 and Batch 2. Our updated batch schedule is below.

Batch schedule

BatchOrdersShips by
Batch 1Early Bird backersEnd of January 2027
Batch 2All remaining pre-sale backers, and orders placed by 30 November 2026End of February 2027
Batch 3Orders placed from 1 December 2026, plus Vault Advisor and Founders EditionEnd of March 2027

The year-end holidays also push the schedule back, as our team, suppliers and couriers slow down from late December into early January.

Guardian, the vault application

  • Secrets wiped after use. Seed words, passphrases and wallet PINs are held in self-erasing memory and cleared as soon as they are no longer needed.
  • Seed words hidden while you type. A key shows them only when you choose.
  • No unencrypted leftovers. Files you export open in a private, memory-only folder, so nothing readable is left behind on storage.
  • Your Vault knows its cards. Each Vault keeps a list of its own Vault Cards, and refuses a card wipe that would leave too few cards to recover the vault.
  • Safer documents. Documents and photos now live inside the encrypted vault, and an edit keeps the old copy until the new one is safely saved.

Vault OS, the operating system

  • Safe firmware upgrades. Your Vault will be upgradable over time, adding new security and features without breaking its air gap. You download an upgrade on your own internet-connected computer and save it to a microSD card. When you insert the card, the Vault automatically checks the upgrade's signature against our developer key before installation begins. Every Vault holds two system copies, so a failed or interrupted upgrade always returns to the working version.
  • Locked production system. Read-only and verified: the system refuses any changed file, and USB devices are blocked by default, except approved ones such as the QR scanner.

Internal testing and build procedures

  • A verified build every working day. Each build runs the full automated test suite and comes with a written verification report.
  • 6,800+ automated tests per build, up from 4,500+ in September. The latest build passed every one.
  • Every change reviewed. No change enters a build until an independent review has checked it.
  • Security rules checked by machine. 20 automated checks guard rules such as where a passphrase may be typed and how Vault Cards are written.

Project risks

AI usage limits and frontier model access. Anthropic, the provider of our main AI development tools, changed its billing and usage policies in July 2026. Those changes affect our development more and more as the code base grows. Access to Fable, its latest frontier model, is now limited, and usage is metered in weekly allowances and in short sessions that reset every few hours. When an allowance runs out, development stops until the next period begins, so the project regularly has to pause and wait. We are working around these limits, but they are impacting development times. They do not change the end result or the quality of the code. We are assessing the impact on the project timeline.

Development does not have to stop when we reach these limits. We can keep working by switching to paid usage credits or to Anthropic's API, both billed at standard API rates, but we estimate that would cost upwards of $30,000 to $50,000 USD per month. That cost was not planned for in our budget. When we reach our usage limits, we have little choice but to wait for them to reset.
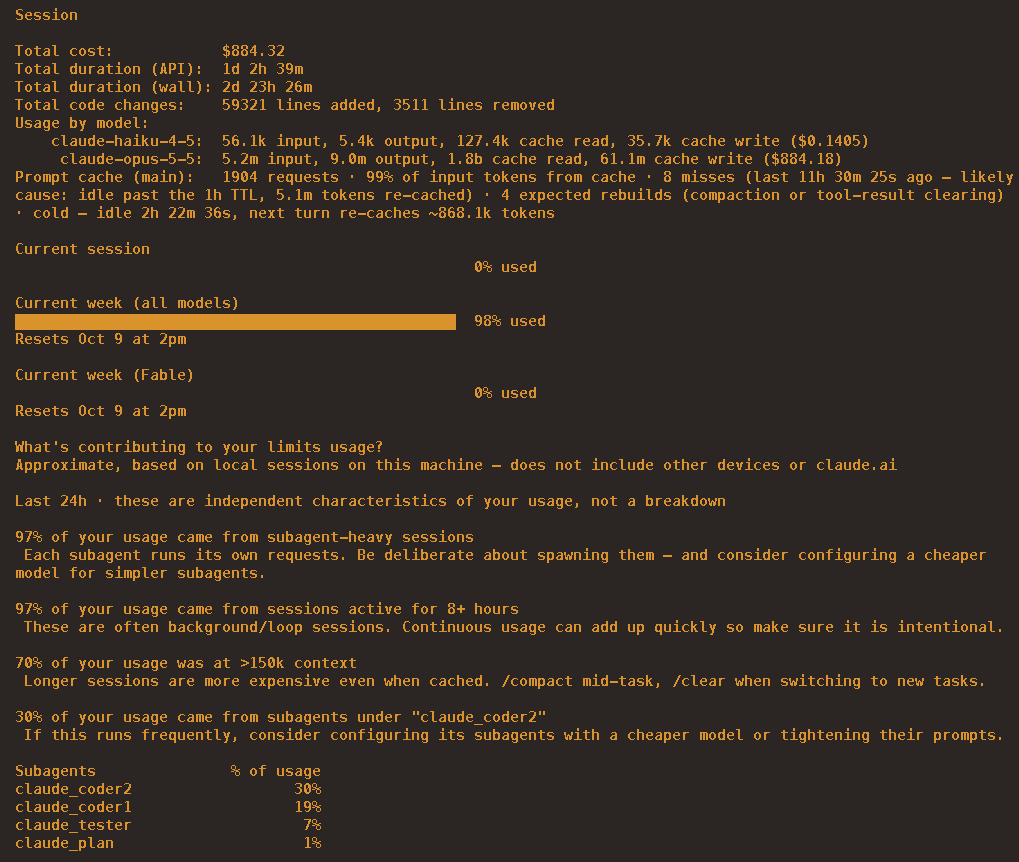
Claude Code usage screen showing the weekly limit at 98% used

Regression testing after foundation changes. Our September rewrite strengthened the Vault's entropy security and changed how keys move securely through the whole application. A change at the foundation reaches many other parts of the code, and each of them has to be adjusted and tested again. This has needed more follow-on changes than we expected.

Progress is slowing as the code grows. Every change now means more code to read, more places it can affect and a longer test run. We plan for that pace rather than cut testing: small changes, tests written first, and nothing enters the daily build unless every test passes.

Project stats

Code base growth. Guardian is now about 235,000 lines of code: 189,000 lines of application and 46,000 lines of tests. Printed at about 50 lines per page, that is roughly 4,700 pages, nearly four copies of War and Peace. At our Prague launch in June it was about 111,000 lines, almost two copies, so it has more than doubled in four months.
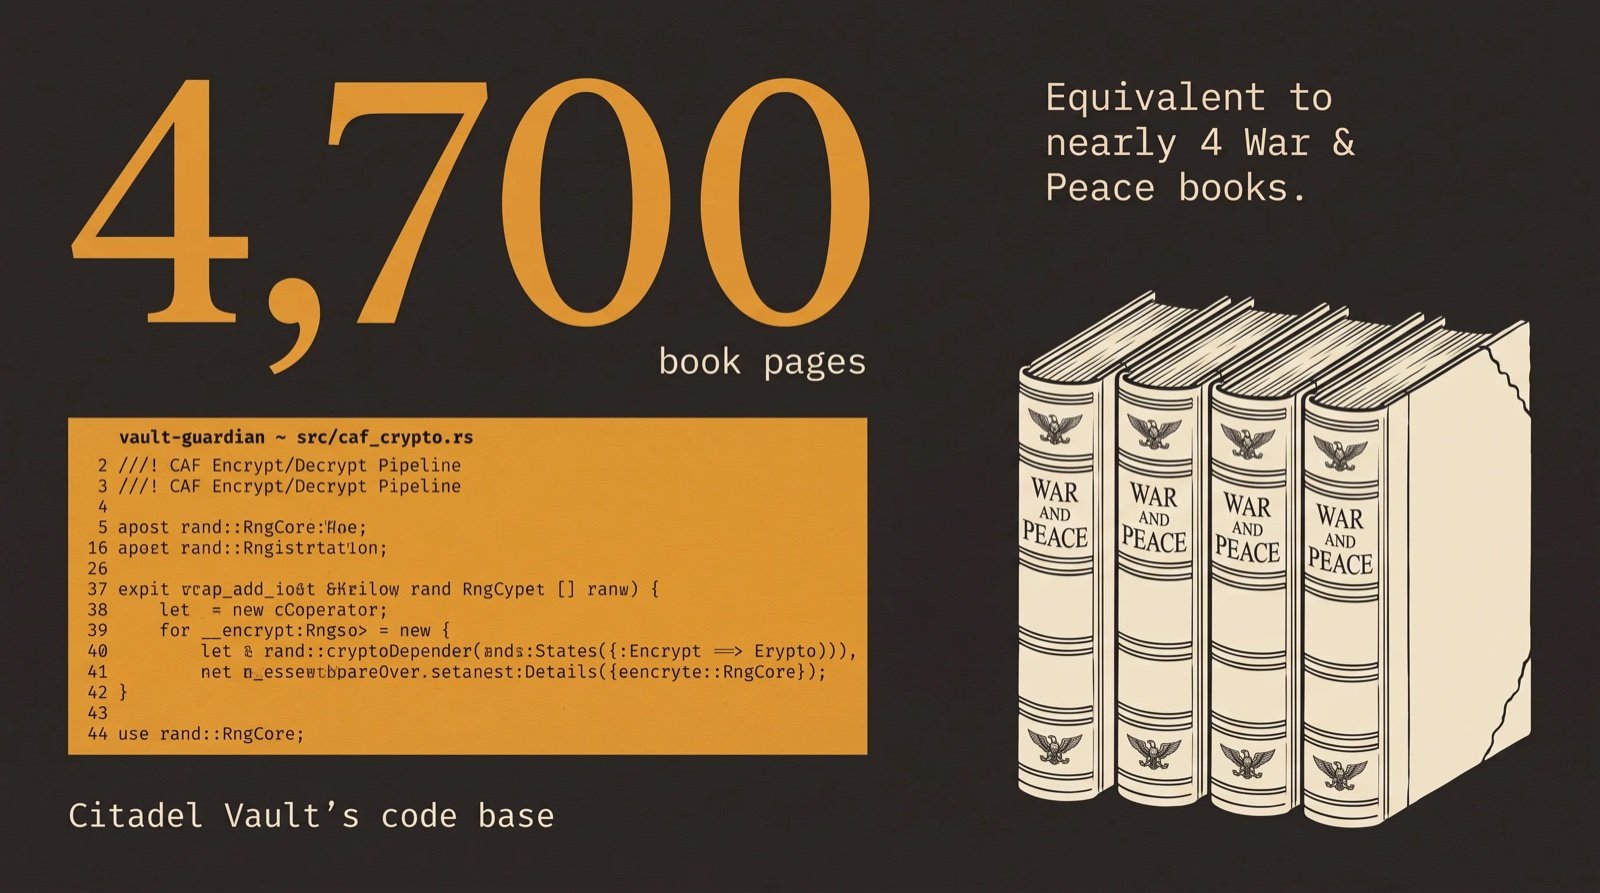
Citadel Vault's code base: 4,700 book pages, nearly four copies of War and Peace

MeasureJune (Prague)October
Lines of codeabout 111,000about 235,000
Printed pagesabout 2,200about 4,700
War and Peace copiesalmost 2almost 4
Tests per buildabout 4,500 (Sept)6,867

AI token usage. We build Citadel Vault with AI assisted engineering, and every change is still reviewed and tested before it enters a build. Since July our AI tools have processed about 24.5 billion tokens, and October alone is on track for about 14.7 billion as we run more coding and review agents side by side.
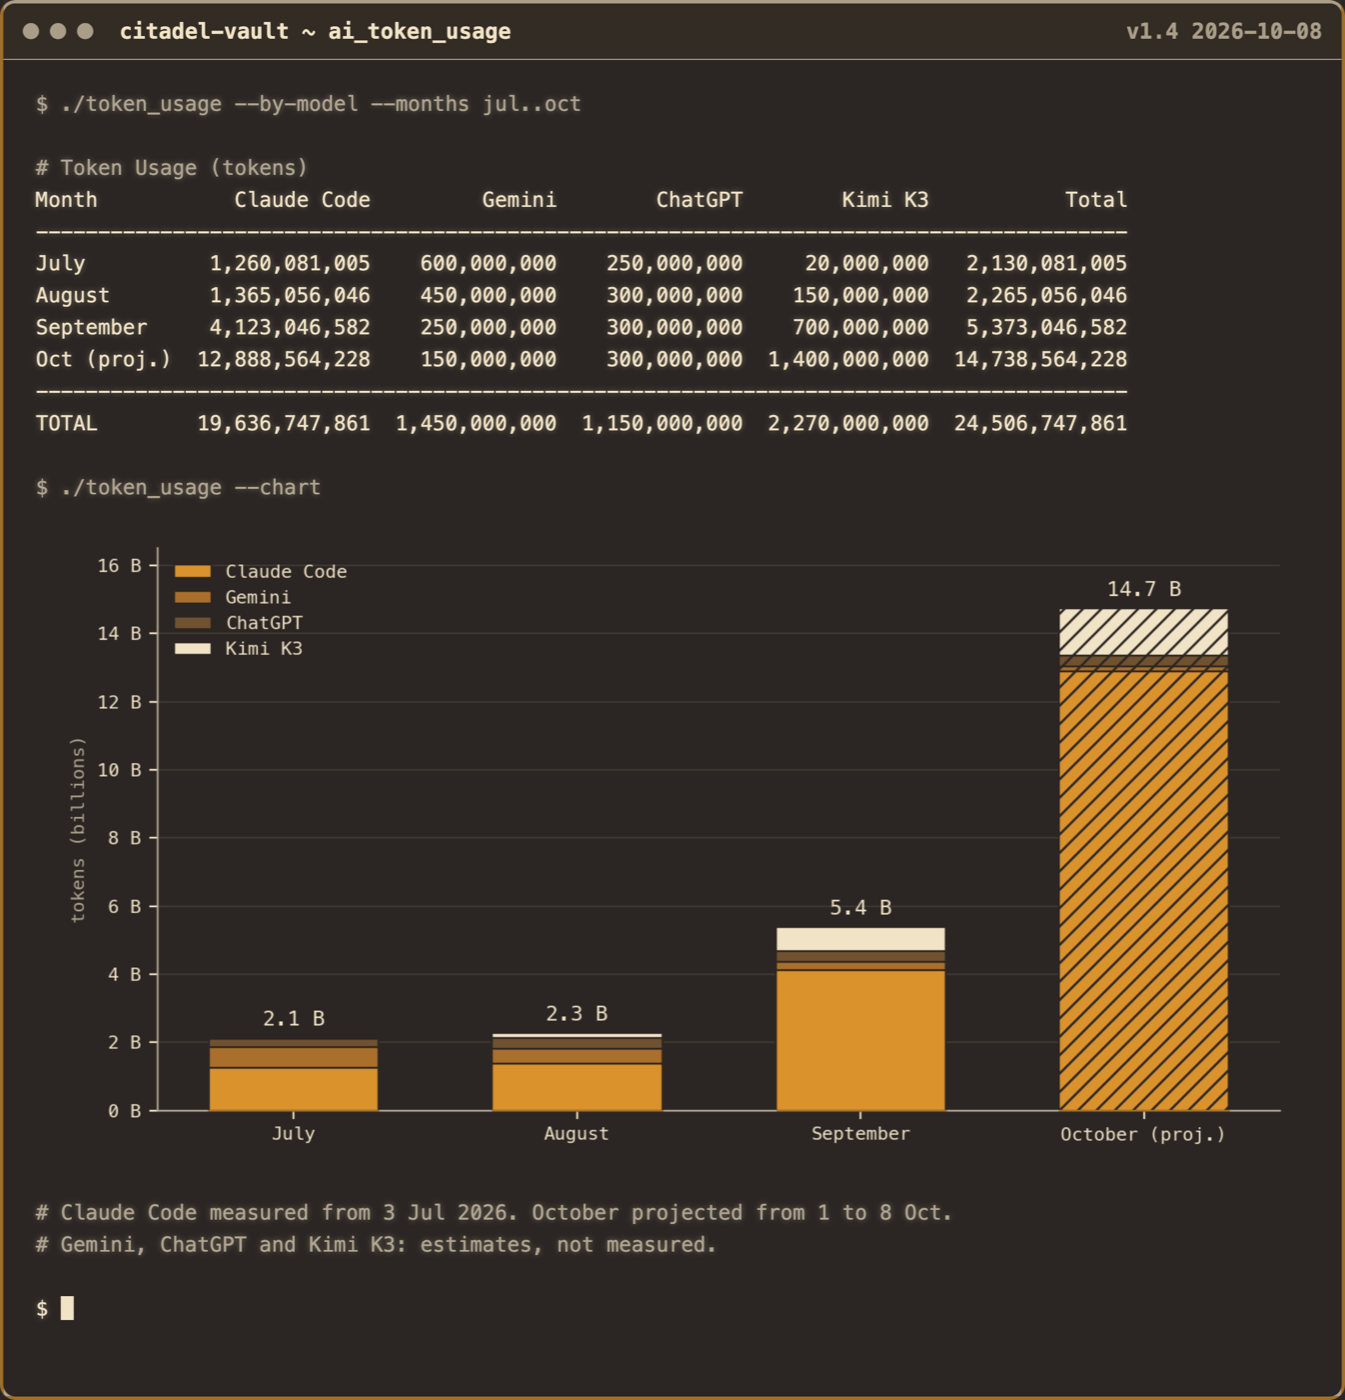
Monthly AI token usage by model, July to October 2026

Next steps

  • Partner demos. Next week we present the Vault to potential partners at two conferences in the U.S.
  • Project update webcast. Join us on Skool on Wednesday 14 October at 17:00 CEST (11:00 New York, 08:00 Los Angeles) for a live project update and your questions.
  • Customer testing. One Vault customer will test a unit in person, and we will invite him to share his uncensored feedback with all customers on an upcoming webcast.
  • More internal test units. Two more units go to our internal testers at the end of October.
  • Reseller flashing tool. We are building a tool that lets our resellers install the Vault software onto units themselves.
  • Updated project plan. We are reworking the plan around the AI usage limits and will share a new delivery schedule for Batch 1 and Batch 2 as soon as it is ready.
  • Vault OS. Work continues with our Vault OS lead developer on safe firmware upgrades and the locked production system.
  • Daily verified builds. Every change keeps going through review and the full test suite before it enters a build.

Questions? Write to us and we will answer directly.

The Citadel Vault Team · Ridgeline Compute LLC · 2026-10-09
2026-09-11 Milestone

Project update: internal test release, the audit, and a look at the setup ceremony

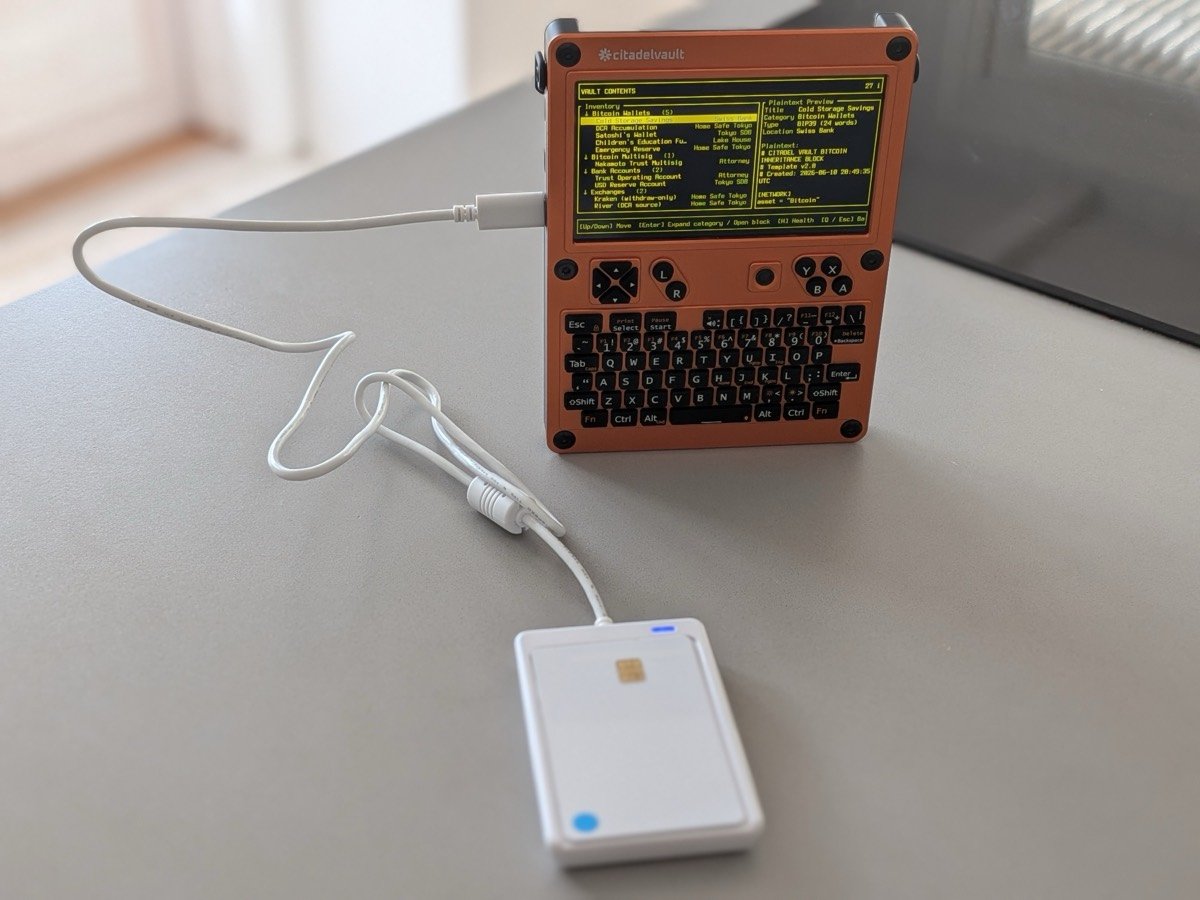
Today we held a project update for customers and resellers, and our internal test release went to the team for testing on the device. The full presentation is linked below. Here is the short version.

Batch 1 is on schedule for the end of October. Warranty and support still start the day your unit arrives. The full delivery schedule on the home page has been updated to match.

An independent security audit covered all three layers: the hardware, Vault OS and the Guardian application. The critical finding was fixed first, and the remaining items are scheduled into upcoming releases.

We are rebuilding the foundation, not patching it. How keys live inside the vault has been reworked so the safe way of handling them is the only way the code allows. More than 4,500 automated tests run on every build.

A new entropy system, in development for Batch 1. Your Vault Master Passphrase will come from several sources of randomness hashed together: the device itself, the chips in your Vault Cards, and your own dice rolls.

We also walked through the setup ceremony screen by screen, showed the expansion boards from their final production run, and the custom foam layout for the vault case.

One point worth repeating: Citadel Vault does not generate Bitcoin seed phrases. It backs up the ones your wallets made, so the flaw that hit Coldcard in July has no equivalent here.

View the full presentation →

Questions? Write to us and we will answer directly.

The Citadel Vault Team · Ridgeline Compute LLC · 2026-09-11

2026-08-10 Schedule

Deliveries move to the end of October: widening our code review

Citadel Vault customer deliveries are moving to the end of October. Internal beta units go out at the end of August as planned, delivered to our own internal team for testing.

The reason is that we are widening our own code review due to recently AI exposed industry vulnerabilities.

In July the Coldcard hardware wallet was found to have generated seed phrases from a software pseudorandom generator, not its hardware random source, and to have done so since 2021. More than $100 million in bitcoin was taken before anyone noticed. The lesson is not that one vendor erred. It is that such a defect can sit in trusted, audited code for years while everyone assumes someone has checked.

What followed says more. Researchers funded by OpenSats, the Bitcoin non-profit, spent hours in early August pointing frontier AI models at 390 open-source Bitcoin repositories.

They filed 4,962 bugs, 85 of them critical bugs, each disclosed privately.

Citadel Vault sits outside most of that. The device has no network stack, so a defect in our code cannot be reached remotely. Exploiting the Vault would require physical possession of your Vault components, and recovery is split so no single component is enough.

That is no reason to assume our code is clean. So before any unit ships, we are giving our own cryptographic code the same treatment, a full review against those same models. It is the reason for the new date, and we would rather absorb the delay than find something later.

Could that failure happen to Citadel Vault?

No, and it is worth being precise about why.

Your seed phrases will always be generated by your own hardware and software wallets. Or you generated seeds manually using dice rolls. Citadel Vault does not create them and is not designed to. Nothing about that failure has an equivalent in how your keys come into existence.

And it is worth repeating: the assets in your Vault never touch the Internet.

The Vault is an air-gapped device. There is no network stack and nothing in the software capable of opening a connection. Recovery never depends on us either, not on our servers and not on our continued existence as a company.

What this means for you

  • Your place in the delivery order does not change.
  • Warranty and support start the day your unit arrives, not the day you ordered, so none of it is consumed by the wait.
  • You will hear from us at the end of August when beta units ship, and again when deliveries begin.

Citadel Vault exists to hold the secrets a family cannot afford to lose, and to pass it along years later to someone who was not in the room when it was created. A product with that job needs to be right.

If this timing creates a real difficulty for your circumstances, reply to this message and we will work it through with you directly.

Thank you for the patience. It is not taken for granted.

Craig, Daniel, Alex, Rex, Mike & Jor

The Citadel Vault Team · Ridgeline Compute LLC · 2026-08-10

2026-07-13 Milestone

BTC Prague launch and hardware finalization

We officially launched the Citadel Vault at BTC Prague and the response was outstanding. The event brought in over 8,000 attendees, which is an excellent turnout for a bear market. Event organizers informed us that our booth saw the top 5% of foot traffic out of 100 vendors. We completely sold out of our Batch 1 units and gathered highly positive feedback to build upon. Ben stopped by the booth while I was speaking and was thoroughly impressed after taking the Vault for a test drive. We also received invitations to speak at Bitcoin conferences and user groups across five European countries. Mike is now leading our enterprise business development, focusing on advisory firms, corporate treasuries, insurance companies, high net worth individuals, and family offices. I am now fully back to writing code and finalizing the software development.

Bill of Materials finalized

On the project development front, we are making steady progress. The hardware Bill of Materials has officially passed its final review.

From NFC to a contact Smartcard reader

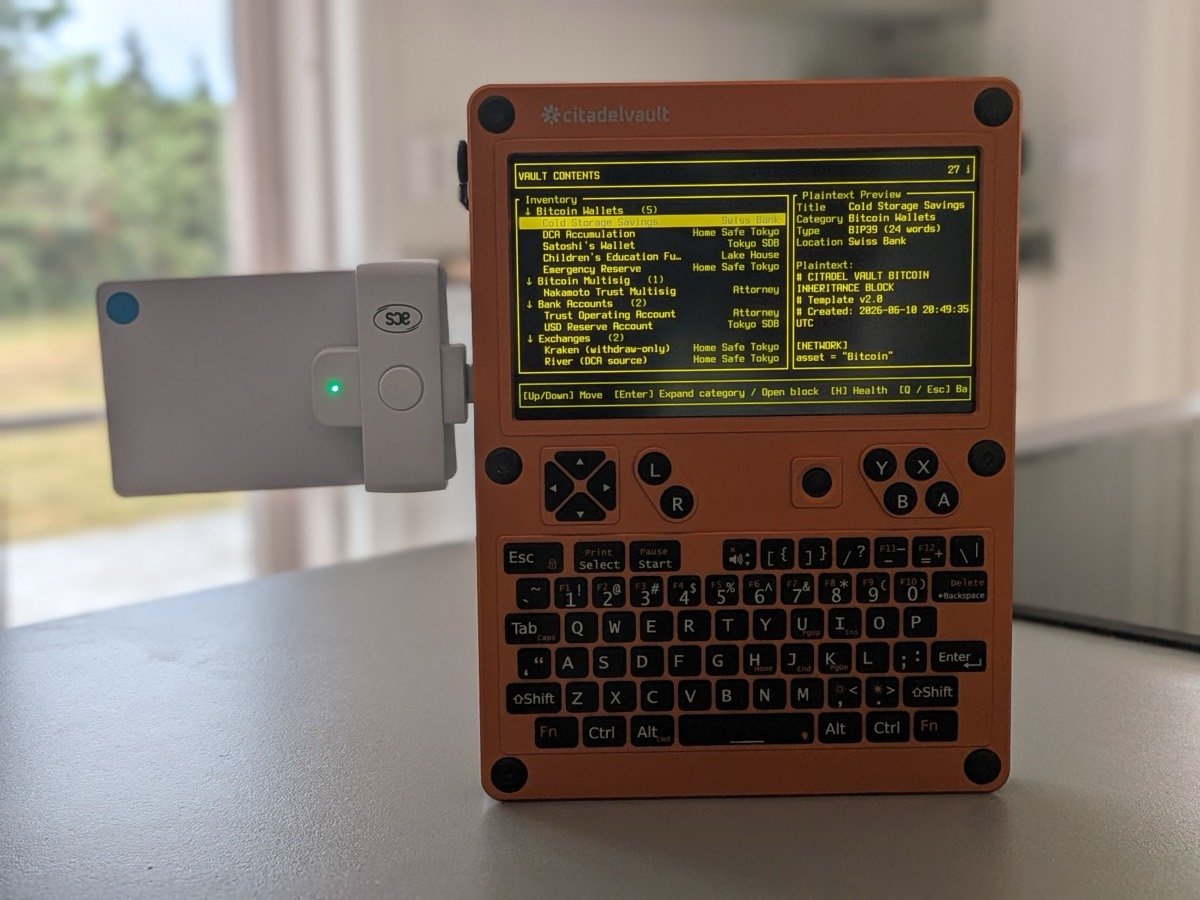
As part of this finalization, we decided to change the Vault Card reader from an external NFC reader to a contact Smartcard reader. Both hardware modules are manufactured by ACS and utilize the exact same driver. This ensures the Vault OS maintains full backward compatibility with the previously issued NFC readers.

The new Smartcard reader provides a smoother and more foolproof user experience. It physically shrinks the security attack surface by completely eliminating wireless NFC communication. The device itself is also physically smaller. Both reader types operate exactly as intended, and you can simply unplug them the moment user authentication is complete using your 2 of 3 or 3 of 5 Vault Cards to unlock the Vault.

Citadel Vault contact Smartcard reader Citadel Vault contact Smartcard reader with a Vault Card

CitadelVault · 2026-07-13

2026-06-12 Milestone

Citadel Vault Timelock, announced at BTC Prague 2026

Securing digital wealth for the next generation has no clean solution. You want your family to inherit your Bitcoin if something happens to you, but you cannot let them access those funds while you are still alive. Citadel Vault solves this with a dead man switch built around a fully offline timelock.

How the Dead Man Switch Works

You configure your Citadel Vault to lock your assets until a specific point in the future. Periodically check in and authenticate with your device, and the Vault pushes that unlock target further down the road. You stay in total control. If you stop checking in, the target time arrives and the Vault enters its recovery phase. Unlike other dead man switch solutions, the Citadel Vault Timelock requires no servers to still be running years or decades later.

The Problem with Normal Clocks

Verifying time on an offline device is harder than it sounds. Standard computers use internal battery-powered hardware clocks. That is a security flaw: anyone with physical access can alter the clock, spoofing the system into believing years have passed to bypass security restrictions.

Citadel Vault contains no internal clock. It is completely blind to the passage of time on its own, so there is nothing for an attacker to manipulate.

Proving Time with Physics

Rather than a hardware clock, Citadel Vault uses the Bitcoin proof-of-work network as an unforgeable timer. Bitcoin produces a new block roughly every ten minutes, and each block requires an enormous amount of physical energy to create.

When the target unlock time arrives, your heirs insert the Citadel Vault microSD card into any internet-connected computer and download the ten most recent Bitcoin blocks. That file goes back onto the card. The Vault reads it and remains air-gapped the entire time.

The Vault calculates the total computational energy required to produce those blocks. Faking that energy expenditure would cost hundreds of thousands of dollars per block. The offline Vault can independently and mathematically confirm that the required real-world time has genuinely passed.

A Trustless Inheritance Layer

Combined, these two features give you an optional but highly secure inheritance mechanism. Your heirs cannot bypass the waiting period by spoofing a local clock: the Vault verifies time against the physical energy of the Bitcoin network. You maintain full authority over your wealth while you are alive. Your legacy transfers safely and verifiably when the time is right.

Citadel Vault is the first solution in the world to offer an air-gapped timelock.

CitadelVault · 2026-06-12

2026-05-19 Milestone

Vault OS: the air-gapped, hardened operating system

Vault OS is the air-gapped, hardened operating system that ships inside every Citadel Vault. It is a stripped-down build of Debian Linux, an open-source, industrial-grade OS that runs much of the world's server and embedded infrastructure. Its job is to check the security of the system and securely boot the inheritance application suite called Guardian.

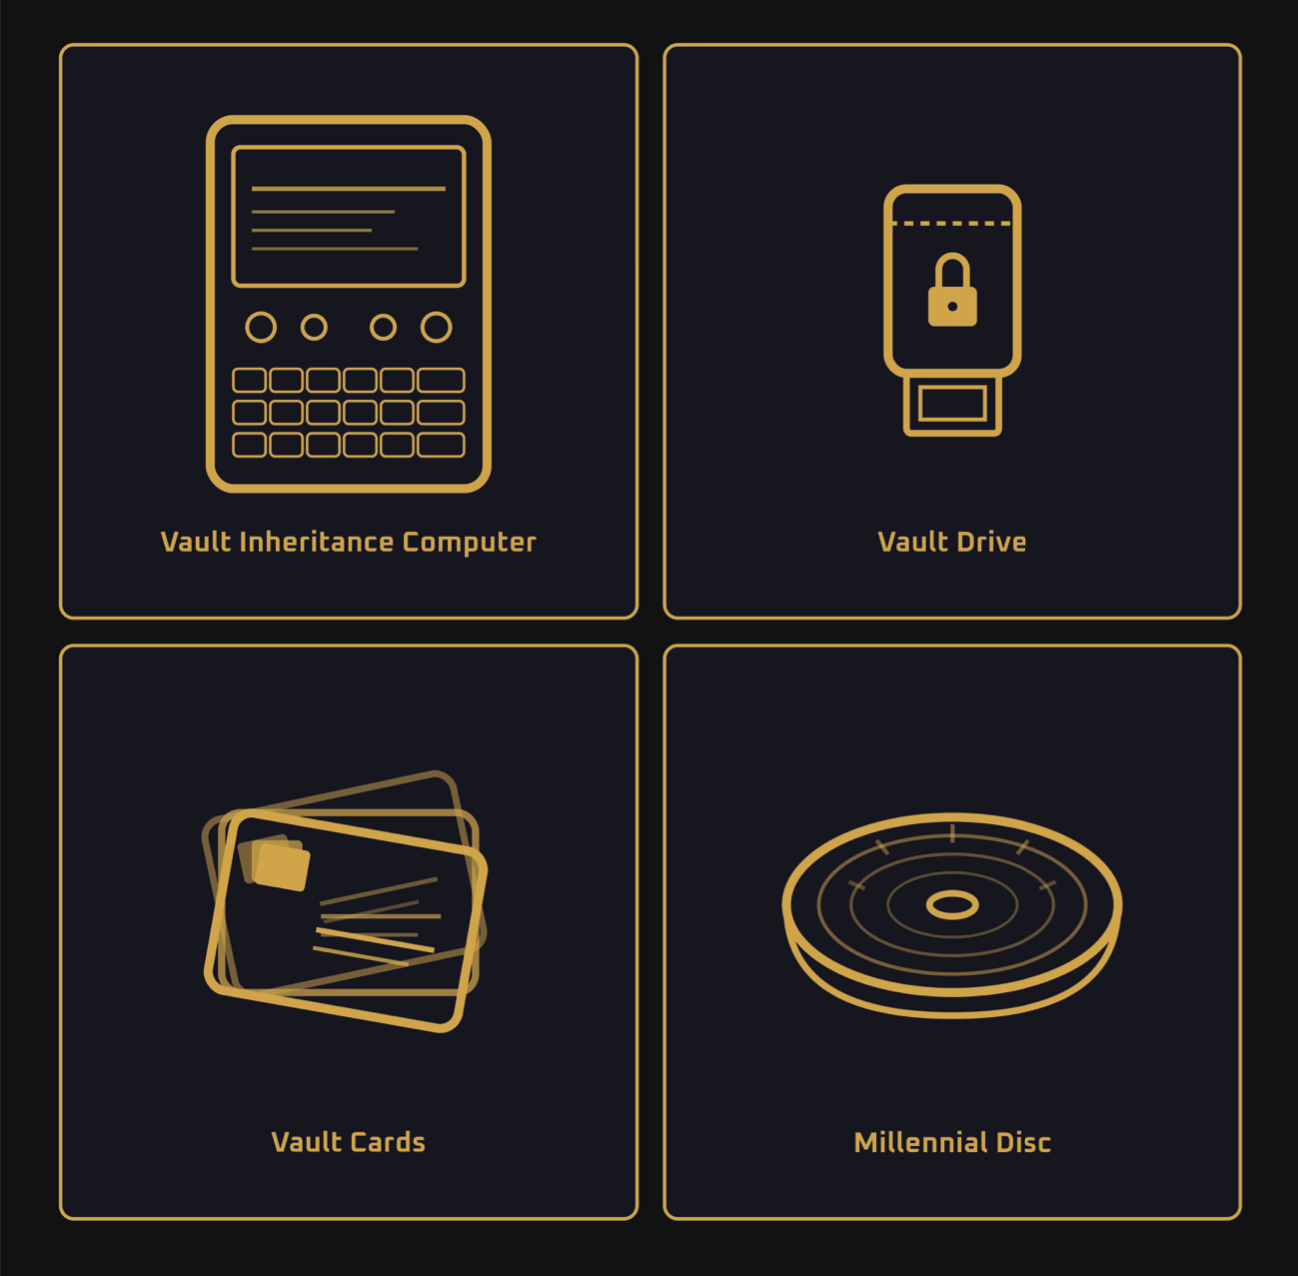
Vault Inheritance Computer, Vault Drive, Vault Cards, and Millennial Disc

Over the past month we reached the milestone we had been pointing at for the better part of a year: the full stack running together on the final hardware. Vault OS boots on the production compute module, Guardian runs on top of it, and a complete working prototype (49 encrypted blocks covering multisig wallets, bank accounts, legal documents, and identity records) can be unlocked using the owner PIN together with 2-of-3 Vault Card verifications. Each Vault Card carries an EAL 6+ certified secure element, and the master passphrase (a BIP39 mnemonic of 12 or 24 words) is sharded across the three cards. Pro, Pro+, Advisor, and Founders Edition ship with five Vault Cards, raising the threshold options to 2-of-4 or 3-of-5. The Advisor and Founders Editions have additional sharding capabilities.

The architecture rests on three tiers: a verified OS image on the compute module inside the Inheritance Computer, customer data encrypted at rest on a removable, industrial-grade USB called the Vault Drive, and the master passphrase that unlocks the Vault Drive sharded across separate Vault Cards. Each tier protects the next. The OS verifies its own state before Guardian boots. The Vault Drive is unreadable without the passphrase. The passphrase exists nowhere on the device, only in the union of cards the owner physically holds. No single tier is enough on its own, and the layers are physically separable so the owner can store them apart.

Milestone arc

Date (2026)Milestone
April 30First successful boot of Vault OS on the production compute module.
May 12Second image, smoke tests on the integrated keyboard and display.
May 16Fourth image, panel and audio paths verified on the final hardware.
May 19Fifth image plus Guardian v2.4.52 installed, Welcome screen end to end, one-key shutdown verified clean.
May 1949 encrypted demo blocks loaded, PIN unlock walkthrough confirmed against the demonstration dataset.

What comes next

  • A production-variant acceptance test of the locked-down image, no developer access, autologin to Guardian, panel-only interaction.
  • Final pass on the four product specification documents for our flagship features ahead of internal review.
  • Last hardware deliveries arriving this week. Then Prague. We will be at BTC Prague June 11 to 13 with a booth, the device, and answers to your questions.

CitadelVault · 2026-05-20